Source NDTV
The Central Board of Secondary Education (CBSE) has admitted to shortcomings in its Online System Management (OSM) portal after a cybersecurity researcher flagged a potential data exposure issue. The incident has raised concerns over the safety of sensitive student and institutional data hosted on the platform.
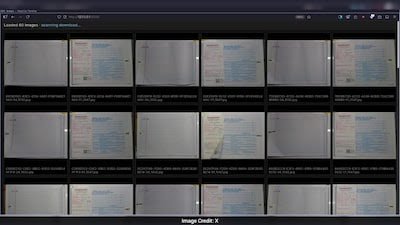
According to initial reports, the vulnerability was identified by an independent ethical hacker who claimed that certain sections of the portal could be accessed without proper authorization. The alleged loophole may have allowed unauthorized users to view confidential information, prompting immediate attention from CBSE authorities.
In response, CBSE issued a statement acknowledging the flaw and confirmed that corrective measures are being implemented. The board emphasized that its technical teams are actively working to strengthen the system and prevent any future breaches. It also assured stakeholders that no large-scale data misuse has been confirmed so far.
Cybersecurity experts have pointed out that such vulnerabilities highlight the need for regular security audits, especially for platforms handling critical educational data. They stress that proactive monitoring and timely updates are essential to safeguard against evolving cyber threats.
The OSM portal plays a key role in managing school-related data, examinations, and administrative functions across CBSE-affiliated institutions. Any compromise in its security could have far-reaching implications for students, schools, and the board’s operations.
CBSE has urged users to remain cautious and report any suspicious activity while reaffirming its commitment to maintaining data integrity and user privacy. Further updates are expected as the investigation into the issue continues.